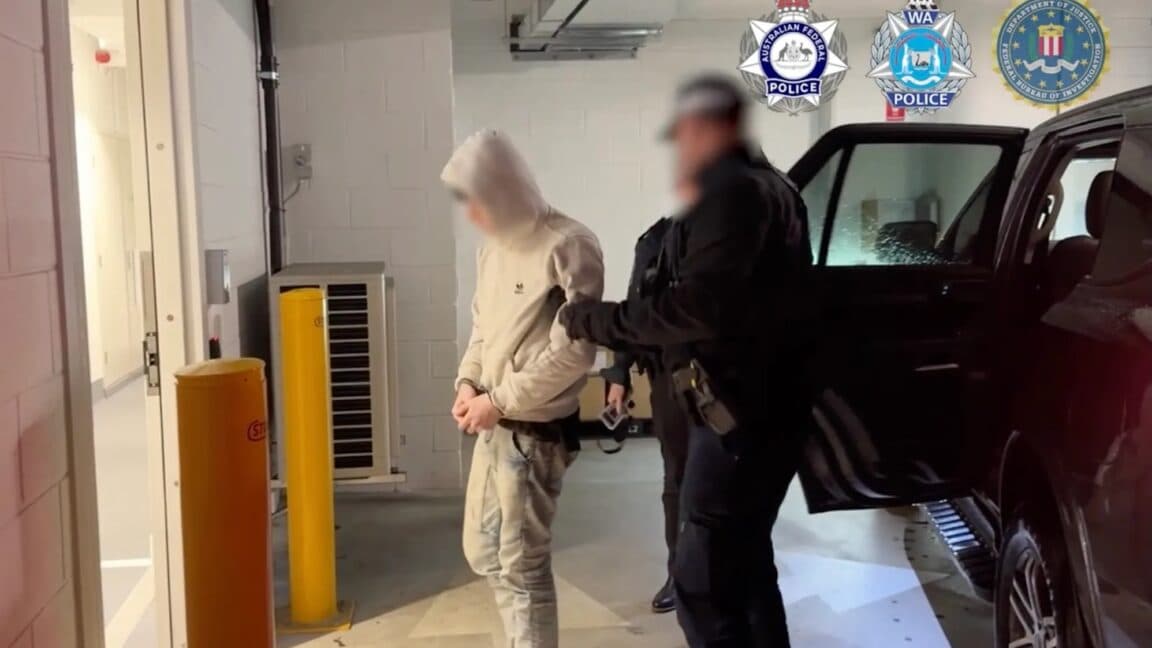
Authorities arrest 2 alleged members of prolific hacking group TeamPCP
Every tech founder loves to fantasize about the mythical adversary: a state-backed actor wielding a bespoke, multi-million-dollar zero-day exploit to quietly slip past firewall perimeters. It sounds s...
Researched and edited by Kiran Ch and the WhatIsFuture editorial team. Reviewed for factual accuracy before publication.
Every tech founder loves to fantasize about the mythical adversary: a state-backed actor wielding a bespoke, multi-million-dollar zero-day exploit to quietly slip past firewall perimeters. It sounds sophisticated, cinematic, and strangely absolving. If a foreign intelligence service burns a novel kernel exploit to crack your infrastructure, nobody really blames the engineering team. But if you spend ten minutes reviewing how groups like TeamPCP actually operate, you realize the ground truth is far more embarrassing. Most multi-million-dollar enterprise intrusions start with a stolen session cookie, an unprotected test database left exposed on an AWS subnet, or a burned-out IT support specialist getting duped over a five-minute phone call.
That is precisely why the recent arrest of two alleged members of the prolific cybercrime syndicate known as TeamPCP hits like a lightning bolt across the security landscape. First broken down in detail by the investigative reporters at Ars Technica, federal and international law enforcement agencies finally cornered key individuals tied to a relentless wave of extortion, SIM swapping, and corporate data theft. While the feds are deservedly taking a victory lap, we need to strip away the sensationalism and look at what this takedown actually reveals. For anyone building modern platforms, managing cloud fleets, or deploying sensitive models, this bust is not a signal that the threat is gone—it is an autopsy of the structural design flaws haunting modern software development.
Join Our Tech Community
Get instant alerts on the most critical AI breakthroughs on our WhatsApp channel. No spam, just signal.
Key Takeaways
- The Myth of the Invincible Threat Actor: The arrest proves once again that even high-profile cybercrime syndicates inevitably crash against the basic friction of operational security (OpSec) errors, Discord paper trails, and financial tracing.
- Identity Is the Only Perimeter That Matters: TeamPCP did not breach targets through arcane cryptographic flaws; they weaponized stolen credentials, exploited weak Multi-Factor Authentication (MFA), and hijacked session tokens.
- The Hydra Problem of Modern Cybercrime: Taking down two high-ranking operators wounds a specific brand, but the underlying economy of initial access brokers, Telegram data shops, and crypto cashout networks remains completely frictionless.
- Actionable Engineering Mandate: Development teams must abandon passive perimeter security in favor of hardware-bound FIDO2 tokens, ruthless token expiration windows, and continuous identity verification.
The Fall of TeamPCP: When Bad OpSec Meets International Law Enforcement
There is a delicious irony in watching threat actors who pride themselves on digital omnipotence get undone by basic human clumsiness. TeamPCP built their reputation on aggressive, smash-and-grab tactics. They specialized in breaking into corporate environments, vacuuming up proprietary databases, exfiltrating internal chat logs, and immediately pivoting to high-pressure public extortion schemes. Unlike old-school ransomware syndicates that quietly encrypt servers and wait for an email, groups in the orbit of TeamPCP rely on public shaming, leaking snippets on Telegram channels, and harassing executive teams directly to force rapid crypto payouts.
Yet, as Ars Technica highlighted in their coverage of the unsealed court filings, running a public campaign of digital extortion is the quickest way to guarantee your own downfall. To maintain leverage in the extortion game, threat actors have to communicate constantly. They run customer support desks for victims, boast on underground forums to build their street credit, and manage complex decentralized teams across multiple time zones. Every single message sent over Telegram, every burner VPN spun up on a compromised server, and every conversion of digital currency creates metadata crumbs. Law enforcement agencies—working across borders through coordinated operations—are exceptionally good at collecting crumbs over eighteen-month timelines.
The authorities did not need to crack commercial-grade encryption to make these arrests. They followed the operational slip-ups: recurring IP addresses exposed during momentary VPN disconnects, reused pseudonyms across clearnet gaming communities, and sloppy cashout attempts on centralized cryptocurrency exchanges. It is the classic paradox of cybercrime: the louder you bark to intimidate corporate victims into paying ransoms, the brighter the spotlight you shine directly onto your own operational infrastructure.
Identity Is the Attack Surface, and Your Zero-Day Paranoia Is Misplaced
Let us be brutally honest about how engineering teams allocate security capital. Boardrooms will happily sign off on half-a-million-dollar AI-powered endpoint detection agents or complex network packet inspectors. Meanwhile, the actual developers are storing hardcoded production API secrets in semi-public testing repos or accepting SMS-based two-factor authentication because "hardware security keys are annoying for developer onboarding." TeamPCP thrived on this specific brand of corporate cognitive dissonance.
When you break down their primary intrusion vectors, you do not see proprietary malware payloads designed to bypass hypervisors. You see social engineering campaigns that target helpdesk staff to trigger unauthorized SIM swaps. You see infostealer logs purchased from darknet marketplaces for fifty dollars, containing persistent session tokens harvested from a remote employee’s malware-infected personal laptop. Once inside, they do not need to exploit vulnerabilities; they simply log in with legitimate credentials, query internal APIs, and harvest customer data using the very tools built to service them.
This dynamic has radical implications as software teams rush headlong into the generative infrastructure wave. We are currently witnessing an unprecedented expansion of cloud footprints, where companies are hooking external APIs into massive compute clusters. We see this scale mirrored in massive capital plays like Anthropic's compute deals with infrastructure providers, showing just how fast and sprawling backend capacity is growing across the sector. If your access management layer treats every authenticated session as inherently trustworthy, handing an identity token to a threat actor like TeamPCP is effectively handing them the master keys to your kingdom.
"We keep trying to solve identity-based attacks with network-based thinking. If an attacker walks through the front door using your employee’s valid session cookie, no firewall in the world is going to raise an alert. You haven't been hacked; you’ve simply been logged into."
The Decentralized Cartel: Why Two Arrests Won't Stop the Bleeding
While the Justice Department and international partners deserve credit for taking these two individuals off the board, viewing this as a definitive victory misses how the cybercrime supply chain works today. Modern cybercrime is not organized like a traditional military unit or a monolithic corporation with a single point of failure. It is an open-source, gig-economy illicit marketplace operating on a franchise model.
In this ecosystem, specialized players handle discrete stages of an attack. You have Initial Access Brokers (IABs) who spend all day scanning for unpatched enterprise gateways or running credential-stuffing campaigns. Once they gain a foothold, they sell that access to groups like TeamPCP. In turn, TeamPCP extracts the data, handles the psychological warfare of extortion, and might contract independent money-laundering rings to run the crypto through mixers and peer-to-peer off-ramps. Busting two members disrupts a specific cell, but the underlying supply chain remains completely operational.
This reality should terrify founders who hold sensitive IP. The commercial stakes are rising dramatically, especially as proprietary datasets, trade secrets, and core models become the primary value drivers for startups. We already know that open-weight AI startups are prime acquisition targets specifically because of their underlying technical assets. If a team leaves an orchestration pipeline or internal dataset unprotected, groups like TeamPCP will not hesitate to hold that training pipeline hostage, leaking proprietary checkpoints to the highest bidder if extortion demands are rejected.
Engineering Lessons: How CTOs Must Architect Against Extortion Syndicates
If you are running an engineering team today, you cannot treat the TeamPCP arrests as mere true-crime entertainment. You need to treat their operational playbook as an audit checklist against your own internal systems. The era of assuming an authenticated user is a benign user has to end immediately. Defending against high-velocity social engineering and credential theft requires structural shifts in infrastructure design, not polite reminders to staff about phishing emails.
First, kill password-only and SMS-backed authentication across every internal surface. If your core systems are not protected by FIDO2-compliant hardware keys—like YubiKeys—that physically resist adversary-in-the-middle phishing attacks, your organization is fundamentally vulnerable. Groups like TeamPCP routinely deploy reverse-proxy phishing kits that capture both the password and the one-time authenticator code in real time. Hardware-bound passkeys break this vector completely by cryptographically binding authentication to the exact domain origin.
Second, enforce aggressive, non-negotiable session token lifetimes. The most devastating enterprise compromises occur because a session token stolen via an infostealer remains valid for thirty days. By enforcing continuous access evaluation, binding tokens to device trust signals, and terminating sessions within hours rather than weeks, you drastically compress the window of opportunity for an attacker. Much like how stability demands modernizing core utilities—a challenge visible when looking at complex infrastructure systems like virtual power networks and aging power grids—software architecture must be redesigned from the ground up for hostile, zero-trust reality.
The Structural Illusion of Corporate Security
The arrest of these two alleged TeamPCP operators will undoubtedly provide temporary relief to corporate boardrooms that found themselves on the group's target list. But celebrating these arrests without overhauling systemic security failures is pure theater. For every cybercriminal arrested because they slipped up on a Discord server or withdrew funds to a KYC-verified exchange, three more are analyzing those mistakes to refine their operational tradecraft.
The digital extortion landscape is sustained not by the technical genius of threat actors, but by the reckless velocity of software development that prioritizes rapid feature deployment over zero
This analysis was inspired by a story originally reported by Ars Technica. Read the original report →
Supercharge Your Workflow with Claude AI
The AI assistant used by professionals worldwide. Write, code, analyse — all in one place.


