Future TechnologyCurated News 2026-10-08 3 min read
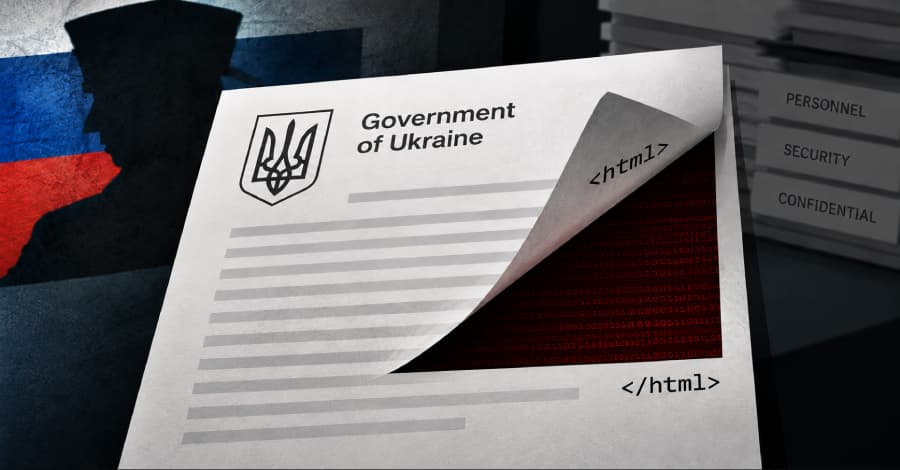
UAC-0099 Targets Ukrainian Government Personnel With ASHVEIN RAT Hiding Commands in HTML
The Russia-aligned threat actor known as UAC-0099 has been attributed to a previously undocumented .NET infostealer and remote access trojan (RAT) codenamed ASHVEIN. According to TrendAI, the malware...
Researched and edited by Kiran Ch and the WhatIsFuture editorial team. Reviewed for factual accuracy before publication.
When I first read the latest TrendAI research on UAC-0099's deployment of the ASHVEIN RAT, my gut reaction was a mix of dark fascination and deep concern. For years now at WhatIsFuture.com, I’ve tracked the relentless game of cat-and-mouse playing out across Eastern Europe's digital frontlines, and this development marks a subtle but dangerous shift. Threat actors aren't just building louder, more complex zero-day exploits; they are mastering the art of hiding in plain sight by abusing the very core markup languages of the open web.
I've been following this for a while now, and what strikes me most is how UAC-0099 continues to outmaneuver conventional endpoint detection without relying on overly
This analysis was inspired by a story originally reported by The Hacker News. Read the original report →
Recommended Tool
Try Claude Free →Supercharge Your Workflow with Claude AI
The AI assistant used by professionals worldwide. Write, code, analyse — all in one place.